Statutory Governance & Client Confidentiality
Privacy policy and personal data management at Ausxconi
Ausxconi (referred to as "we", "us", or "our") operates the website ausxconi.com and delivers independent cryptocurrency tax compliance, forensic ledger reconciliation, and ATO audit representation services. We are dedicated to safeguarding the privacy and personal data of our website visitors and clients in accordance with the Australian Privacy Principles (APPs) set out in the Privacy Act 1988 (Cth). This policy outlines our procedures regarding the collection, handling, storage, and protection of personal information.
Statutory Disclosure Schedule
Information collected through this website and service engagements
Under our professional obligations and client intake mandate, Ausxconi collects information strictly necessary to provide comprehensive crypto tax compliance, portfolio reconciliation, and advisory services. We do not aggregate speculative market profiles or harvest data beyond legitimate taxation and statutory defense requirements.
Identification Details
- Full legal name & title
- Postal & residential addresses
- Primary email & direct phone
- Verified date of birth
Regulatory Information
- Tax File Numbers (TFNs)
- Australian Business Numbers (ABNs)
- Australian residency declarations
- Corporate ACN credentials
Financial & Ledger Data
Cryptographic transaction ledgers and fiscal records necessary for forensic cost-base reconstruction:
- Public blockchain wallet addresses
- On-chain transaction hashes (txids)
- Digital exchange trade archives
- Prior notices of assessment
Technical Connection Data
- Client IP address records
- Browser agent & OS profile
- Access timestamps & session tokens
- Form submission diagnostic logs
Ausxconi never requests, collects, or retains private cryptographic keys, seed recovery phrases, or exchange operational withdrawal credentials. Our advisory procedures rely exclusively on public ledger data, view-only API synchronization, and exported read-only CSV trade statements.
Intake verification conducted at Suite 405, 530 Collins Street, Melbourne.
Consent & Channel Integrity
Methods of personal information collection
Personal information is collected directly from you when you complete website intake forms, schedule consultations, communicate with our staff, or provide financial transaction ledgers. We prioritize direct customer transparency and verify client authority prior to ingesting ledger documentation into our tax computation engines.
We do not collect personal information about you from third parties without your explicit prior consent, except where authorized or required under Australian law. Such statutory exceptions include:
Direct statutory data retrieval from the Australian Taxation Office Online Services for Agents portal following execution of your signed Tax Agent Appointment Authority.
Transmission of prior accounting workpapers or trust deeds directly from your designated external solicitor, estate trustee, or commercial auditor upon written direction.
In compliance with APP 5, whenever Ausxconi collects personal information directly from you, we provide a contemporaneous notification detailing our identity, the specific operational purpose, and your statutory rights to access the records.
Statutory Operational Mandate
Purpose of data collection and usage
We collect, hold, and process your personal information exclusively for lawful professional purposes, ensuring absolute compliance with federal taxation legislation and regulatory standards governing registered tax practitioners.
ATO Lodgment & Statutory Preparation
Preparing, reviewing, and lodging individual, corporate, trust, and Self-Managed Super Fund (SMSF) income tax returns and capital gains tax schedules with the Australian Taxation Office.
Forensic Ledger Reconstruction & Software Cleanup
Conducting forensic blockchain ledger reconstructions, software reconciliation, wallet synchronization, missing cost-base resolution, and technical asset position assessments across multi-chain ecosystems.
ATO Audit Defense & Dispute Representation
Representing you in formal reviews, risk-differentiation framework responses, comprehensive audits, objection submissions, and formal dispute proceedings before the Australian Taxation Office.
Mandatory Legal & Anti-Money Laundering Compliance
Complying with statutory reporting, verification, and ethical duties under the Tax Agent Services Act 2009 (TASA) and the Anti-Money Laundering and Counter-Terrorism Financing Act 2006 (AML/CTF Act).
Engagement Administration & Statutory Deadlines
Communicating with you regarding engagement progress, forensic deliverables, advisory updates, service invoicing, and statutory tax lodgment cutoff dates throughout the Australian fiscal calendar.
Handling of Tax File Numbers under statutory rules
Your Tax File Number is handled with heightened legal protection in accordance with the Privacy (Tax File Number) Rule 2015 issued under the Privacy Act. We recognize the profound sensitivity of federal tax identifiers and enforce strict procedural firewalls surrounding TFN handling.
We will never use your TFN as an internal client identifier, and we will never disclose your TFN to unauthorized third parties. TFN information is transmitted exclusively to the ATO through encrypted, secure government portal connections.
TFNs are never indexed in marketing engines, client relationship databases, or public correspondence. TFN fields are redacted upon completion of statutory workpaper archiving.
Lodgments and TFN transmissions operate over dedicated TLS 1.3 cryptographic pipes directly interacting with ATO machine-to-machine (M2M) authenticated gateways.
Privacy (TFN) Rule 2015 Provisions
Infrastructure Resilience
Storage and information security controls
We maintain physical, technical, and administrative safeguards to protect your personal information against misuse, interference, loss, unauthorized access, modification, or disclosure. Transaction ledgers and tax records are stored in encrypted cloud environments located within Australian data centers. Access to client data is strictly restricted to authorized personnel who require access to perform professional tax services.
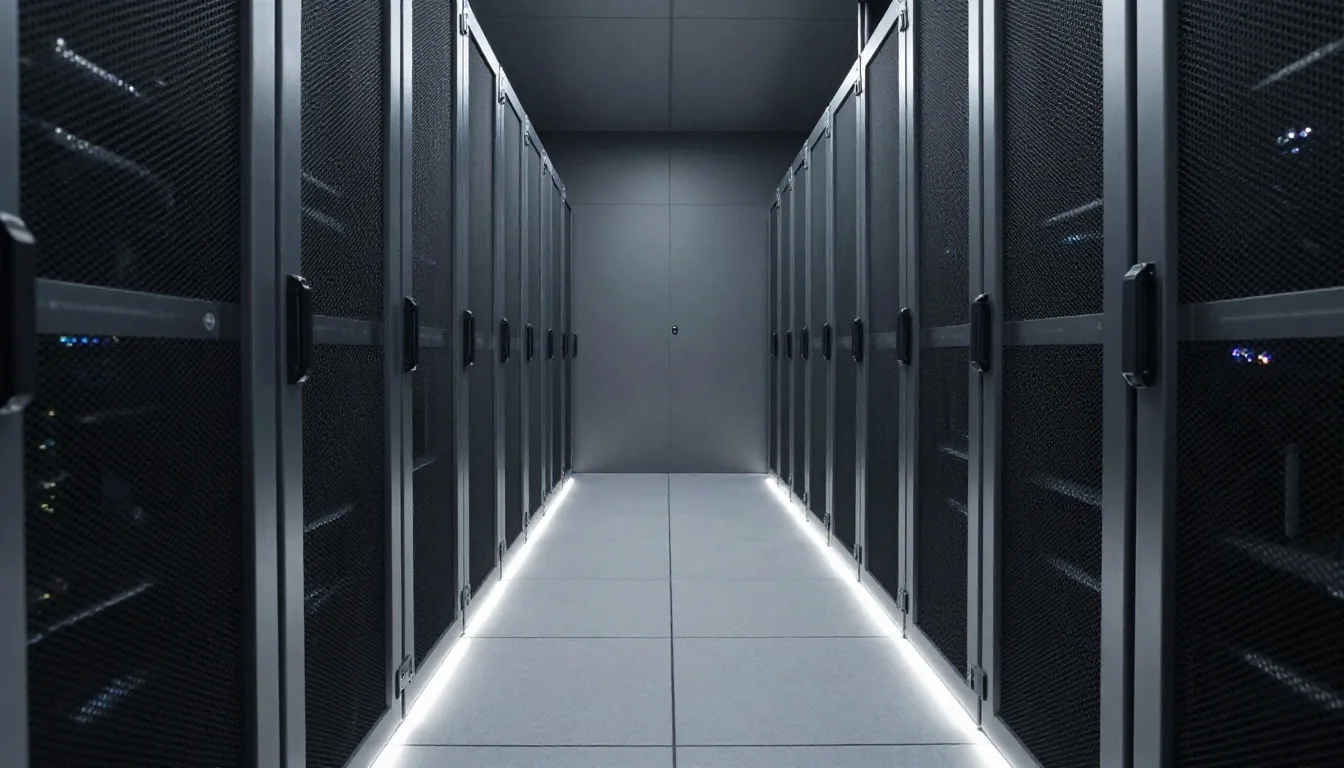
Data Sovereignty Within Australia
All primary databases, document repositories, and ledger analysis stores reside exclusively in certified Australian data centers located in Melbourne and Sydney. We do not mirror unencrypted financial records to overseas cloud tenancies or multi-region routing hubs subject to foreign disclosure mandates.
Military-Grade Cryptographic Controls
Records are protected using AES-256 bit encryption at rest, with cryptographic keys managed under dedicated hardware security modules (HSMs). All ingress and egress traffic between client endpoints and Ausxconi servers enforces TLS 1.3 encryption with strict HTTP Strict Transport Security (HSTS).
Least-Privilege Administrative Governance
Staff permissions are governed by role-based access controls (RBAC) and hardware-token multi-factor authentication (FIDO2/WebAuthn). Access logs are maintained immutably, ensuring full traceability of every file access, reconciliation execution, and document download.
Strict Disclosure Boundaries
Disclosure of personal information to third parties
Ausxconi will never sell, lease, or trade your personal information to third-party commercial entities, broker lists, or marketing databases. We treat client information with the confidential sanctity demanded of registered tax practitioners under the Tax Agent Services Act 2009.
Statutory Regulatory Agencies
Disclosures made directly to the Australian Taxation Office (ATO), the Tax Practitioners Board (TPB), or other law enforcement and regulatory authorities where:
- • Explicitly authorized by you under an engagement letter;
- • Required pursuant to formal statutory notices under Section 353-10 of Schedule 1 to the TAA 1953; or
- • Compelled under valid judicial warrant or court subpoena.
Approved Specialized Tax Engines
To verified software service providers, secure document repositories, and specialized blockchain reconciliation engines under strict contractual non-disclosure agreements (NDAs) that mandate:
- • Complete data confidentiality covenants;
- • Total prohibition on secondary data mining;
- • Enforced cryptographic deletion at task completion; and
- • ISO 27001 or SOC 2 Type II compliance standards.
Designated Client Counsel
To your designated external legal counsel, commercial accountants, SMSF auditors, or accredited wealth managers, conducted solely:
- • Upon receipt of your prior written instructions;
- • Under certified professional legal privilege rules; and
- • Through encrypted transfer protocols with verified receipt tracking.
Statutory Record-Keeping Mandate
Data retention and statutory archiving periods
Under Section 262A of the Income Tax Assessment Act 1936 (ITAA 1936) and professional regulations established by the Tax Practitioners Board, we are required to retain client tax workpapers, transaction records, reconciliation ledgers, and lodgment receipts for a minimum of five (5) years from the date of the relevant ATO assessment or transaction completion.
Following the expiration of the statutory retention period, personal records are securely deleted or irreversibly de-identified using certified cryptographic sanitization standards (NIST SP 800-88 Rev. 1), ensuring no remnant fragments can be reconstructed.
Active File
Preparation, client review, and formal lodgment through ATO portal.
Statutory Archive
Encrypted cold storage for statutory audit defense and amendment periods.
Purge / De-Identify
Irreversible cryptographic deletion or complete data de-identification.
"A person carrying on a business must keep records that explain all transactions and other acts engaged in by the person that are relevant for any purpose of this Act."
Retention duration measured from the precise date of ATO notice of assessment issuance.
Zero file residual recovery; permanent physical or cryptographic sanitization.
Australian Privacy Principles 12 & 13
Accessing and correcting your personal information
You have the right to request access to the personal information we hold about you and to request corrections if you believe the data is inaccurate, incomplete, or out of date. We are committed to prompt resolution under statutory timeframes.
Submit Written Request
Send your written request to our designated Privacy Officer at [email protected], specifying the exact records, correspondence, or ledger reports you wish to inspect or correct.
Statutory 30-Day Response
We will acknowledge receipt and provide access to the requested records within 30 calendar days, subject to statutory exemptions permitted under the Privacy Act (such as legal professional privilege or ongoing ATO audit investigations).
Rectification & Notification
If any personal information is proven inaccurate, incomplete, or out of date, we will rectify our internal ledgers immediately and formally notify any relevant statutory bodies or third parties previously provided with the data.
Statutory Clarifications
Frequently asked privacy & data compliance questions
Clear answers regarding client confidentiality, ATO data matching protocols, and your legal safeguards.
Does Ausxconi share my crypto wallet addresses with the Australian Taxation Office automatically?
No. Ausxconi operates strictly as an independent professional advisory firm. We do not provide automated data feeds or live wallet inventories to the ATO. Information is submitted to the ATO exclusively as part of client-authorized formal tax lodgments (such as Capital Gains Tax schedules) or during formal, client-mandated audit defense representation where you have executed an explicit authorization letter.
How does Ausxconi comply with the Privacy (Tax File Number) Rule 2015?
We isolate Tax File Numbers within encrypted database fields with restricted cryptographic permissions. We never utilize your TFN as an internal client account code, and it is never displayed on routine invoices, engagement letters, or non-lodgment workpapers. In strict alignment with the Privacy (TFN) Rule 2015, TFNs are transmitted solely through the ATO's secure M2M Agent portal endpoints.
Can I request that Ausxconi delete my financial records immediately after my tax return is lodged?
While you have the right to request deletion of non-essential marketing or correspondence records, Australian taxation law overrides general erasure rights for professional tax workpapers. Under Section 262A of the Income Tax Assessment Act 1936 and the Tax Agent Services Act 2009, registered tax agents are legally obligated to retain tax return source documents, lodgment receipts, and ledger calculations for five years from assessment. Once this statutory period concludes, records are permanently sanitized.
What happens in the unlikely event of an eligible data breach?
Ausxconi maintains an active Incident Response Plan compliant with the Notifiable Data Breaches (NDB) scheme under the Privacy Act 1988. If an incident involving unauthorized access or loss of personal data occurs that poses a likely risk of serious harm, we are legally mandated to notify the Office of the Australian Information Commissioner (OAIC) and all affected individuals promptly, providing detailed mitigation guidance.
Lodge a statutory access request or privacy enquiry
For all enquiries regarding your personal information, requests for record access or correction under the Australian Privacy Principles, or questions regarding our statutory compliance protocols, please reach out to our designated Privacy Officer.
If unresolved, complaints may be escalated to the Office of the Australian Information Commissioner (OAIC) at oaic.gov.au or by phoning 1300 363 992.